An audit trail for AI coding agents.
Who approved it, what it cost, and can you prove it? Ticinuum writes each state change and the event that describes it in one database transaction, to an append-only timeline — so the record of what an agent did can't drift from what happened.
Early access ↓Audit trail
Every diff, decision, token, and dollar — on the record.
A state change and the event that describes it are written in one database transaction. Most event systems are eventually-consistent and can drift from reality. This one can't.
State changes and their events are written in the same PostgreSQL transaction, so the timeline can never diverge from reality.
- An append-only timeline — of everything that happened — relayed to an analytics store with at-least-once delivery and dedup.
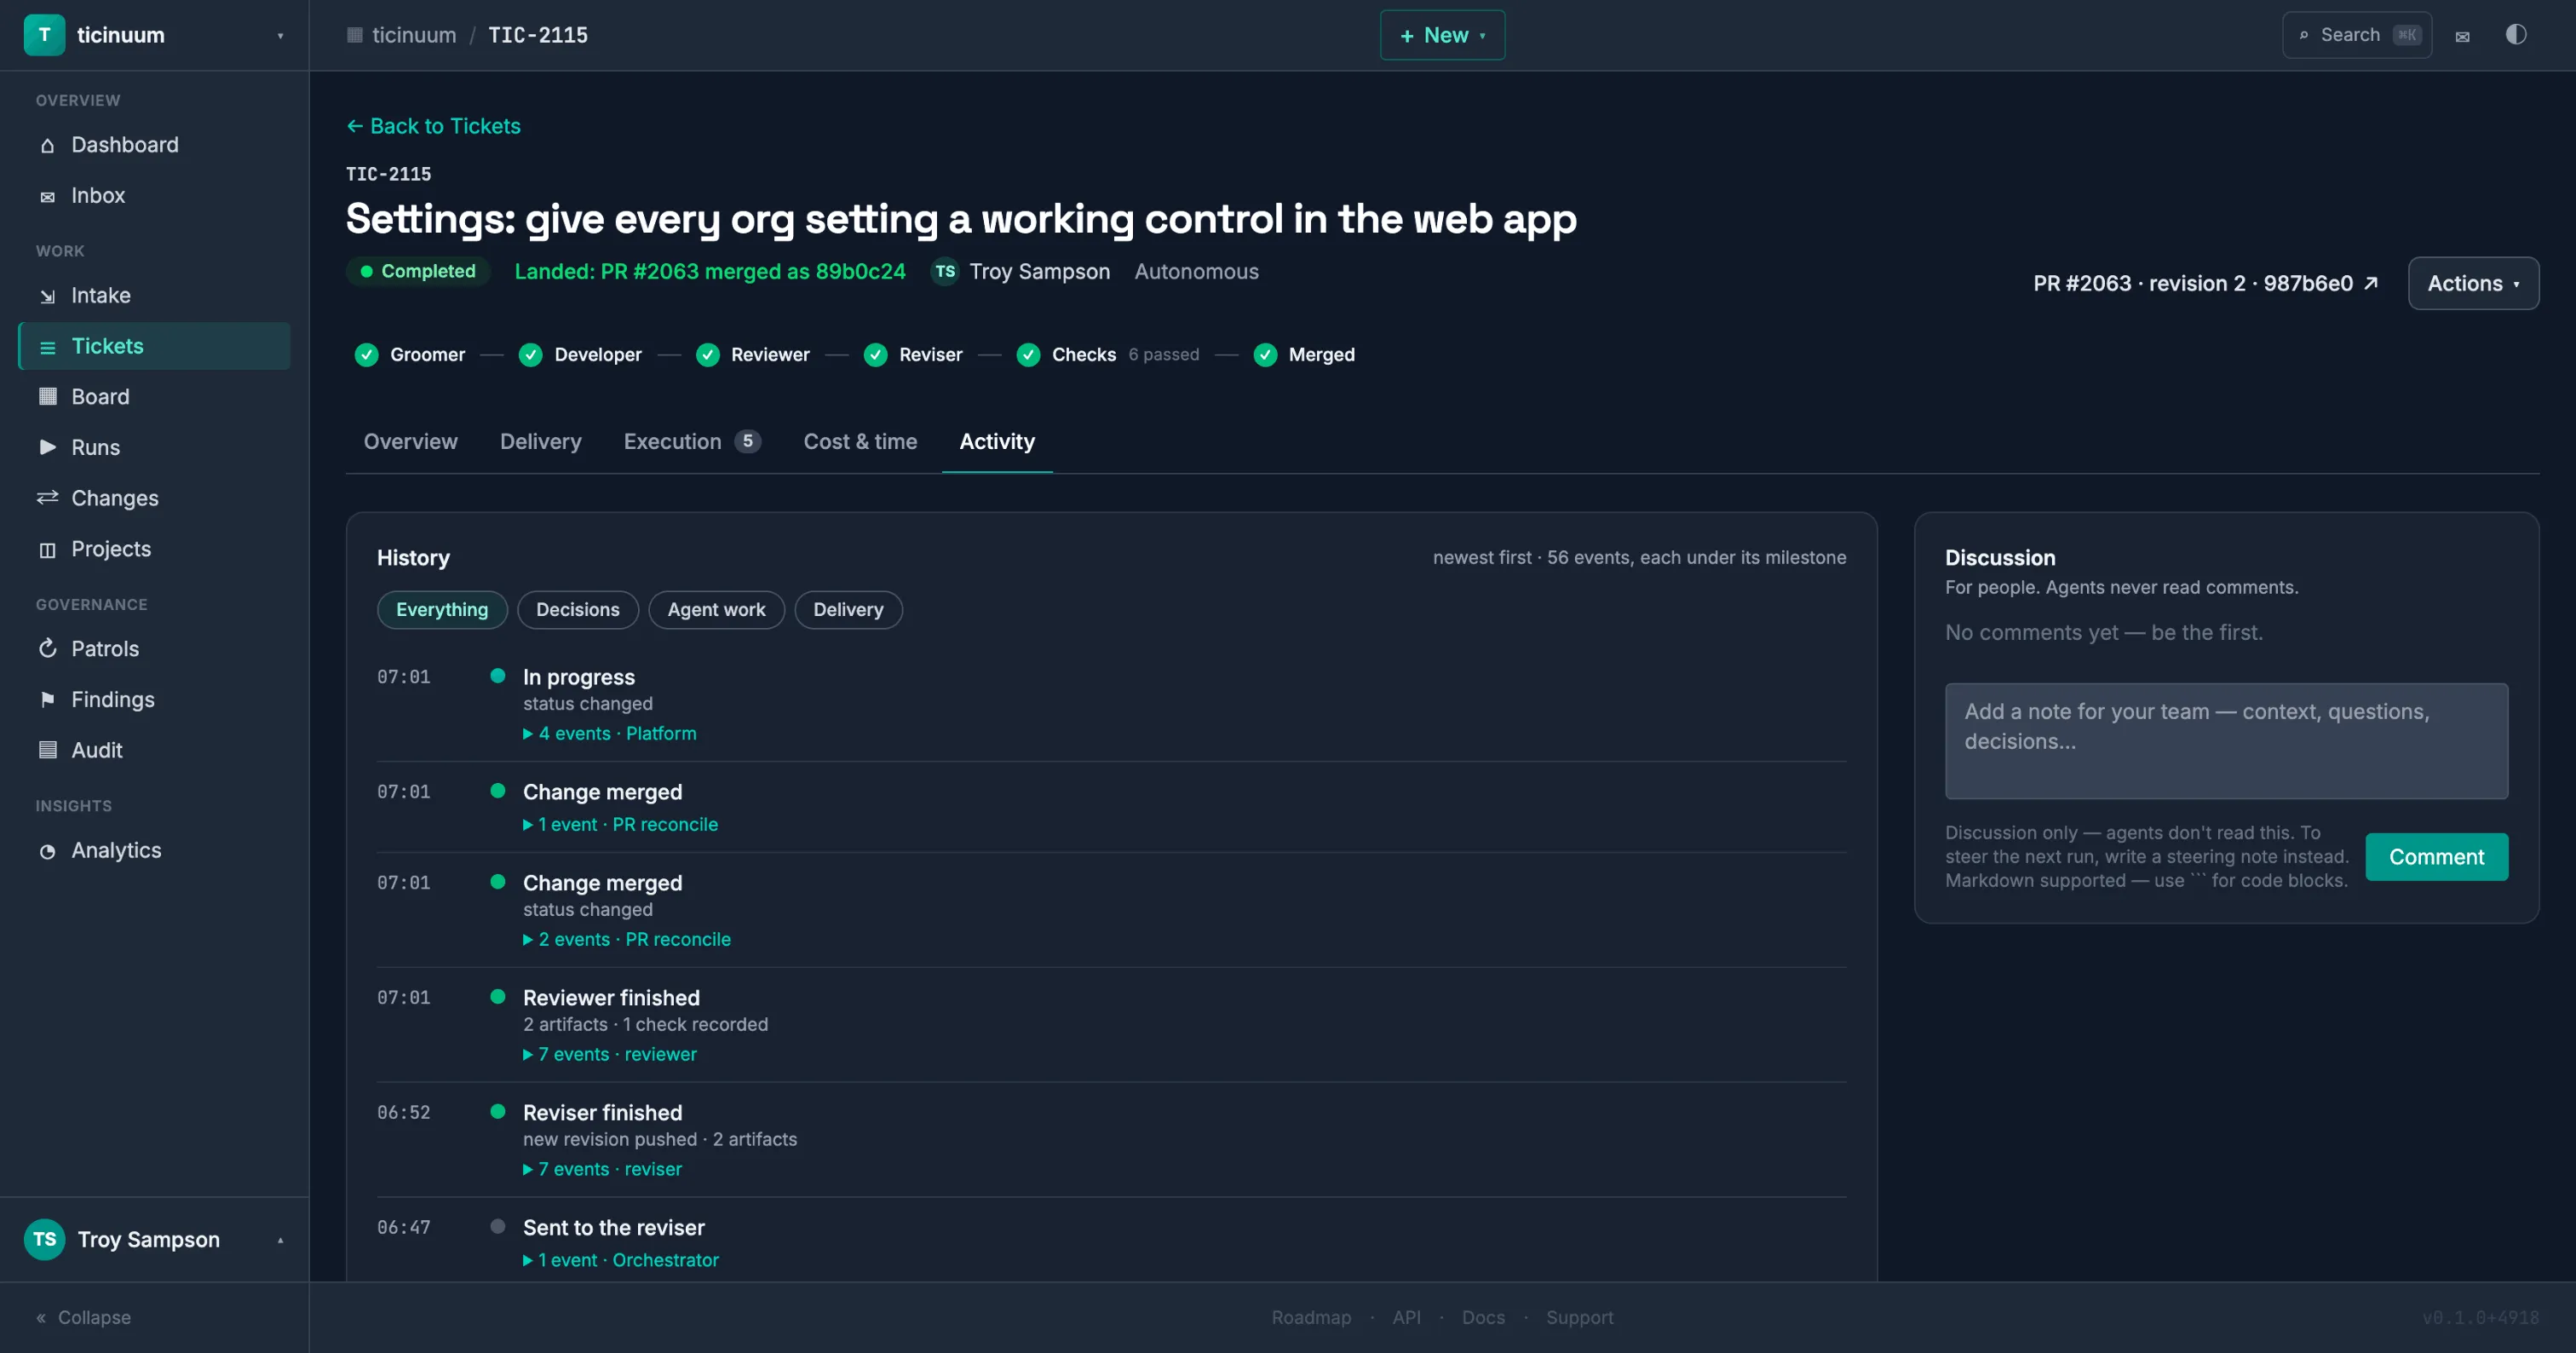
- Every token and dollar — per ticket and per run — metered from real input/output counts and stored, surviving later price changes. Each ticket shows where its money went, by token class, and — once your org has enough finished work to compare against — how far it has drifted from what similar work usually costs and takes.
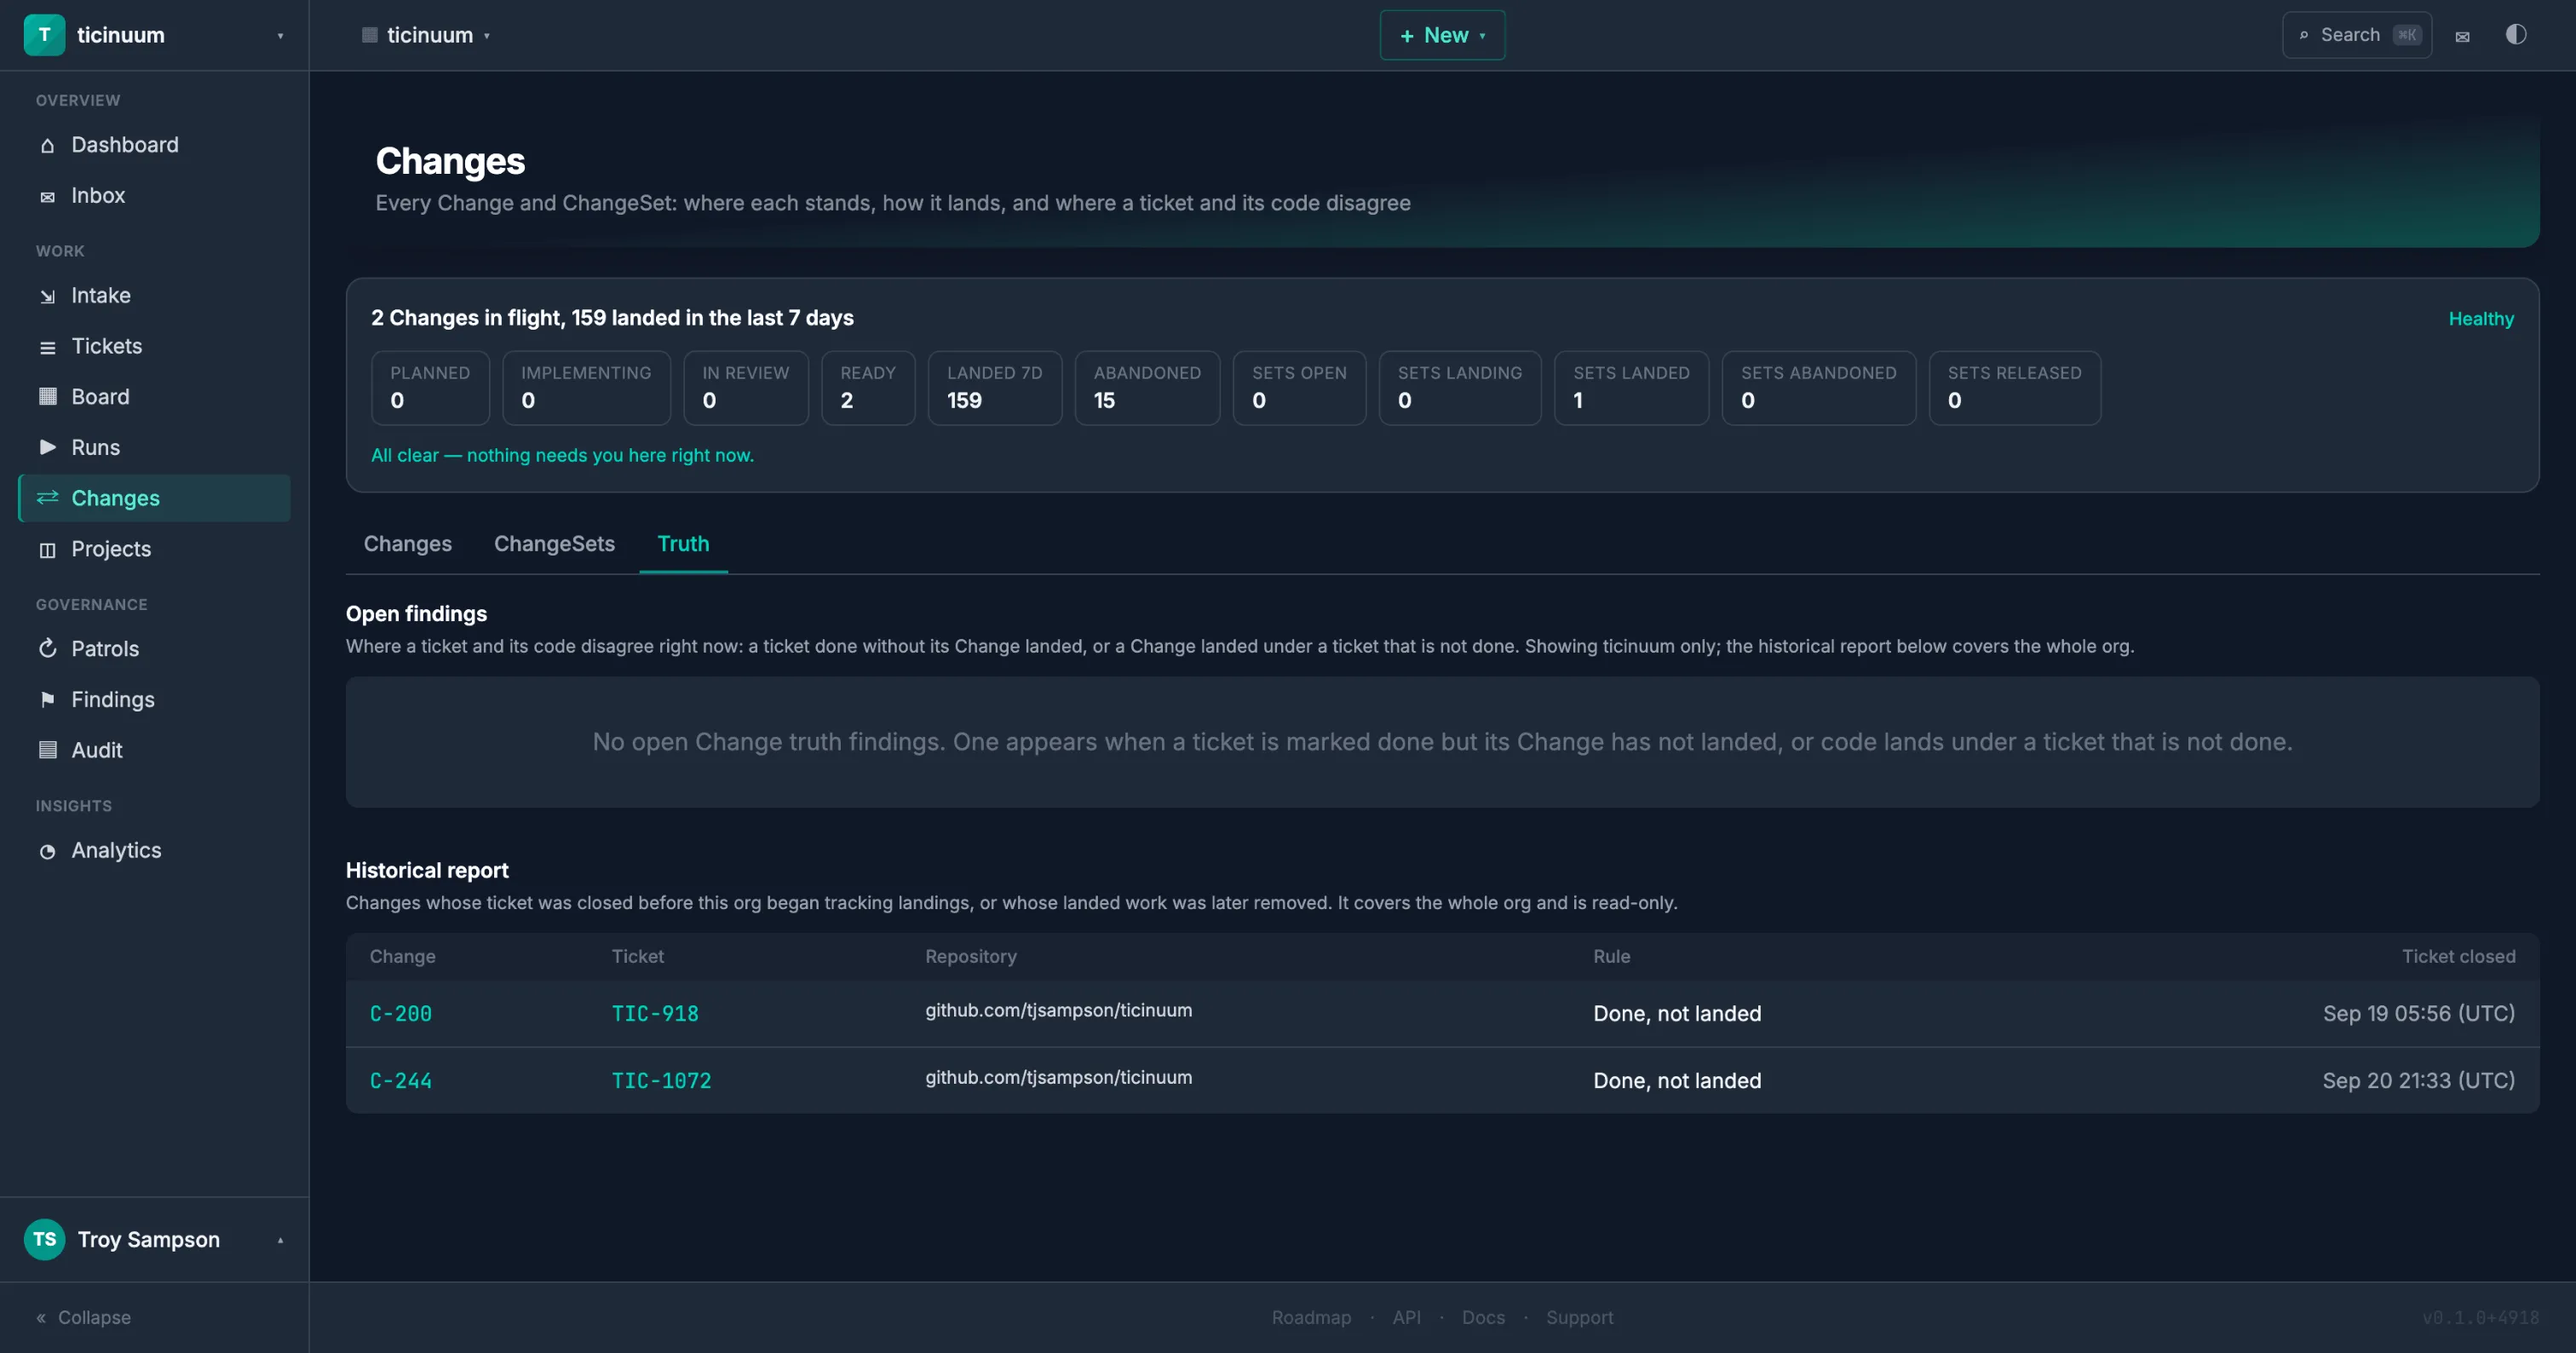
- The agent's report, beside what was verified — a ticket's page sets the agent's own account next to the facts the platform recorded for itself — the pull request's state, the review's verdict and how much of the change it read, the checks — so a confident summary never stands in for evidence. A Truth view lists every ticket marked done whose code never landed, and every change that landed under a ticket that isn't done.
- A live tail of the agent at work — stream the real run's iterations, tool calls, and pauses to the ticket view — like CI logs, for the agent — then archived to blob storage.
- Export the whole ticket — one self-contained .tar.gz bundle — a markdown summary (spec, PRs, reviews, cost, comments, timeline), every run's full log, and the artifacts — to hand a local model or keep as an audit artifact.
- Run logs, diffs, plans, and snapshots — in durable blob storage — ours by default, or yours (see Data residency below).
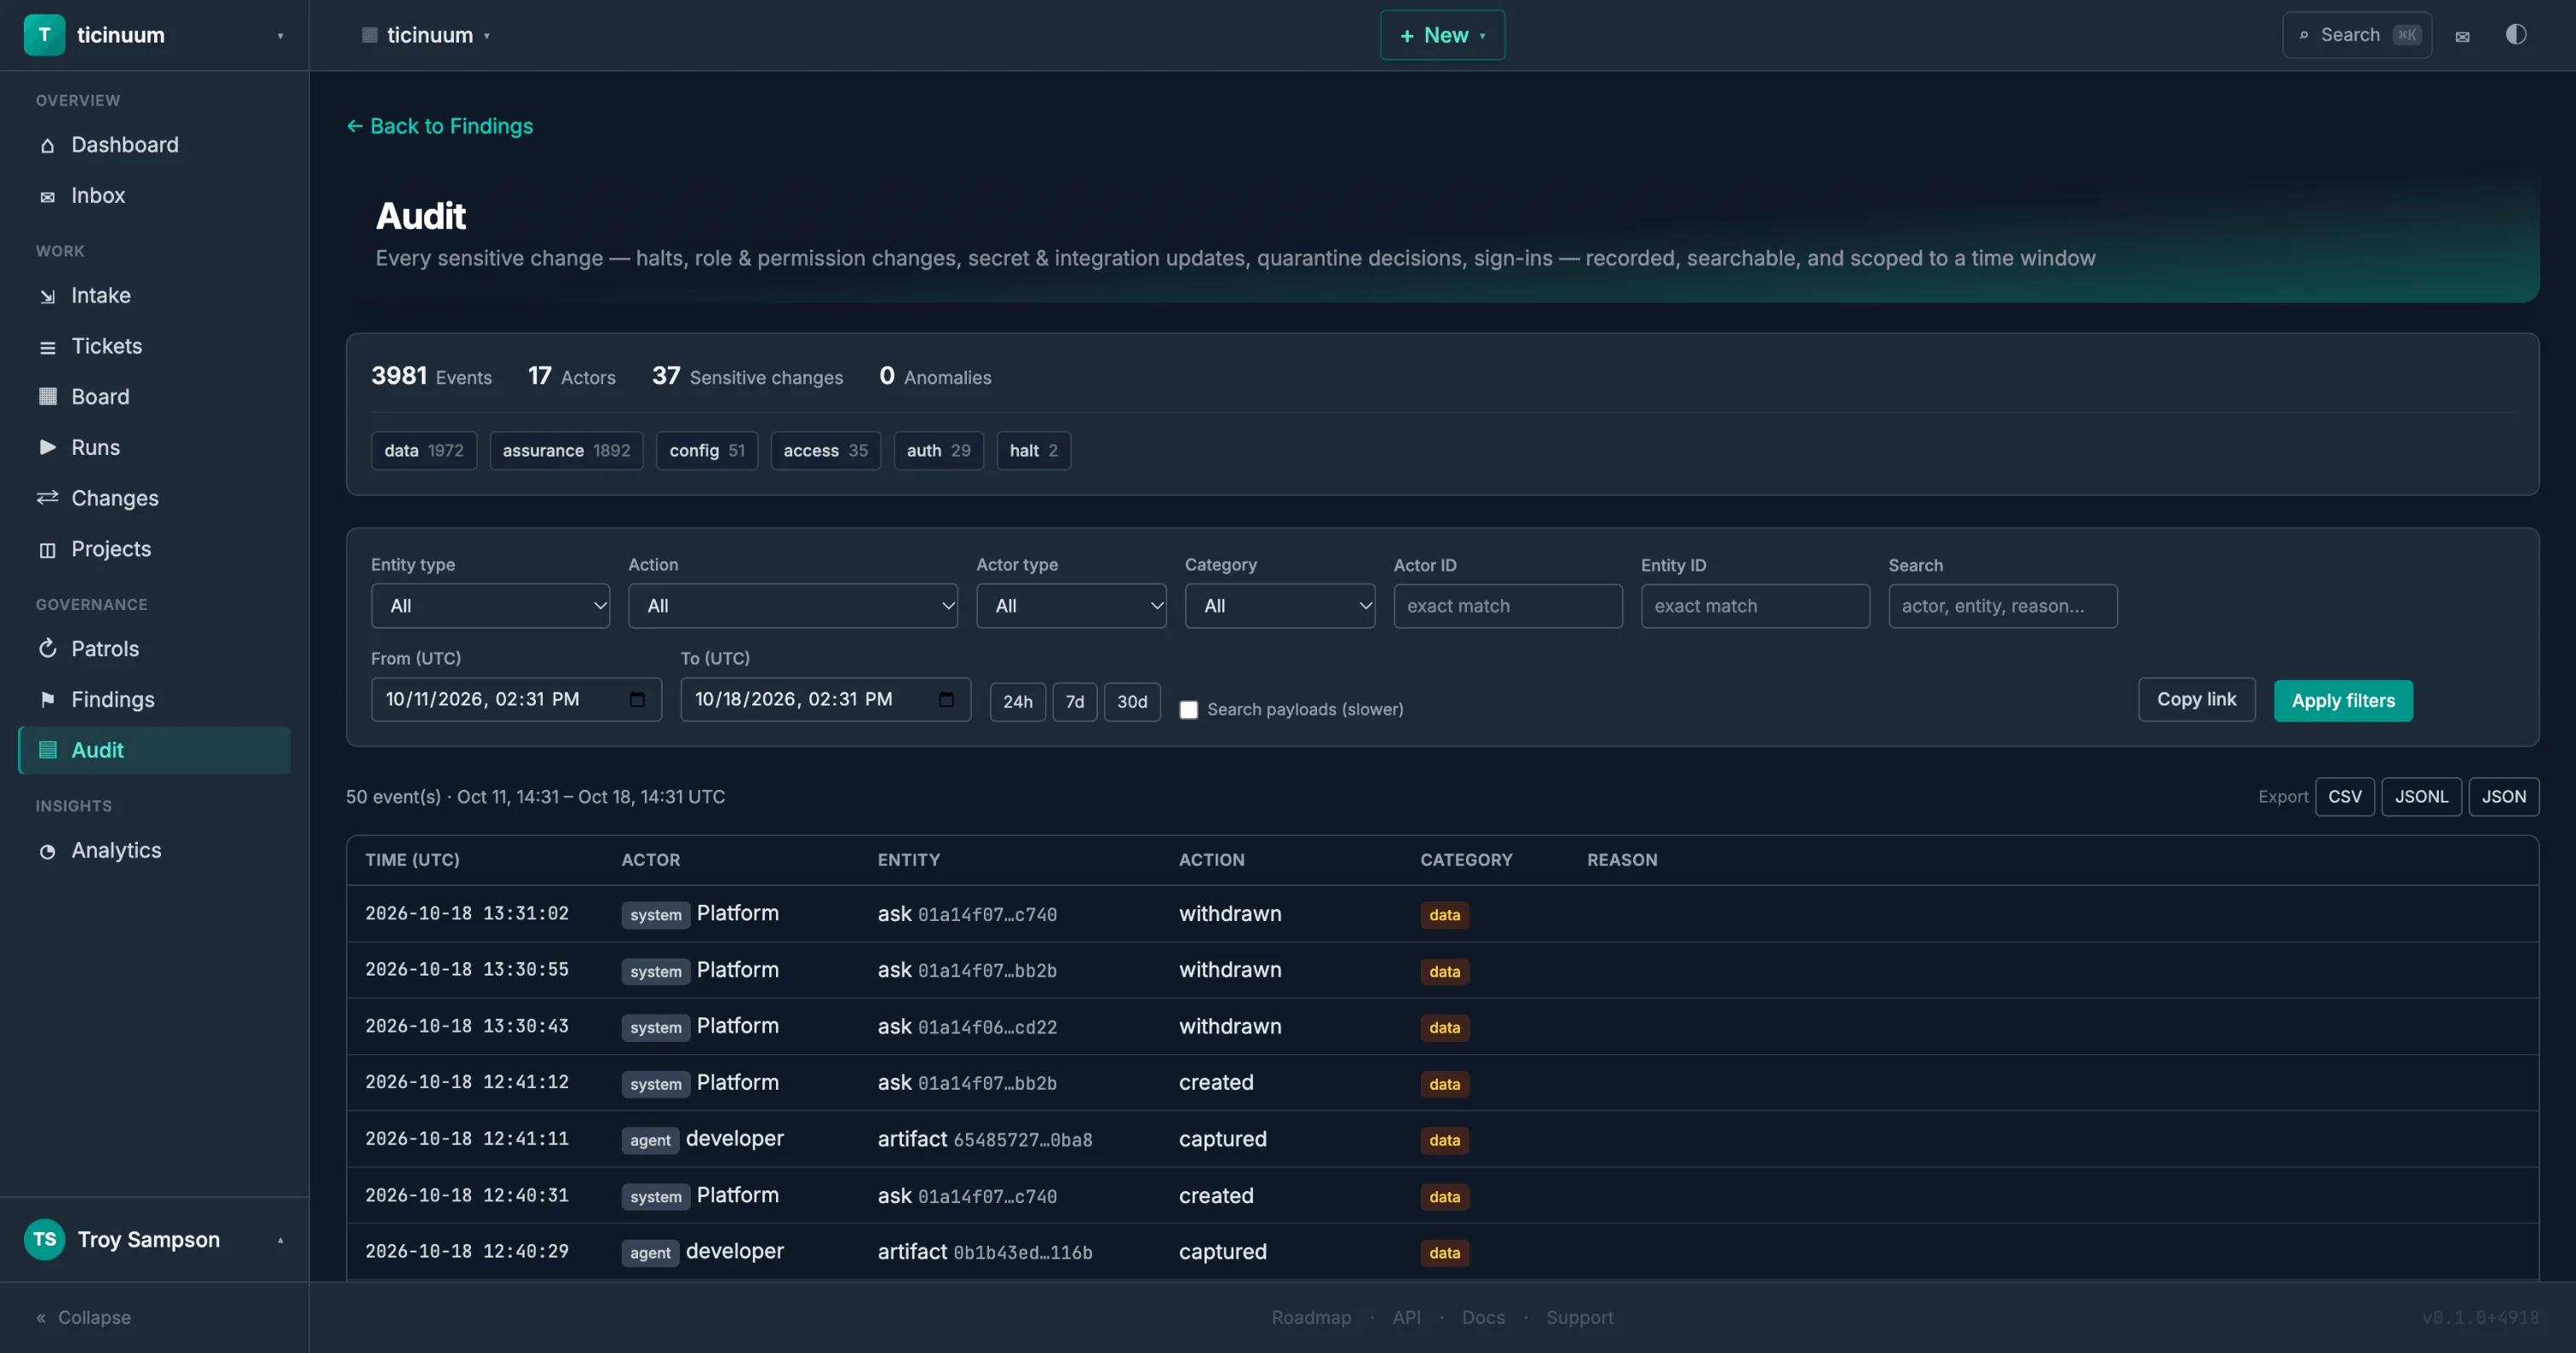
- A searchable, tamper-evident audit view — sensitive changes beyond the ticket timeline — kill-switch flips, role and secret changes, quarantine, logins — land in an append-only audit stream, hash-chained per org and re-verified on a schedule so an altered or missing row shows. Filter it by entity, actor, action, and time at /ui/audit: an OrgAdmin over their own org, a SystemAdmin across every org. A streaming CSV/JSONL/JSON export of exactly the filtered slice is an admin-gated toggle, on by default.
- The evidence an audit actually asks for — every interaction logged; a reviewer running in a fresh context.
In the product
Captured from the product.
Real screens from Ticinuum’s own organization, taken in October 2026 — not mockups.
FAQ
Questions, answered plainly.
Can I see and export the audit trail?
Yes. Sensitive changes — kill-switch flips, org halts, role and secret changes, quarantine, logins — land in an append-only audit stream, hash-chained per org and re-verified on a schedule. Each change is written in the same transaction as the state it describes, with one deliberate exception: engaging a halt or a budget pause commits first and audits a moment later, so a stop can never fail because its log line did. Admins browse it in an Audit view with structured and free-text filters and per-row before/after drill-down; a streaming CSV / JSONL / JSON export of the filtered slice is available (on by default, and an admin can close it). Org admins see their own org; system admins see across orgs.
Are you SOC 2 certified?
No, and we won't claim a status we don't have. What's true today: state changes and their events written atomically, a hash-chained audit stream, AES-256-GCM key encryption, revocable sessions, app-layer tenant isolation (404), and a two-layer injection gate.
The rest of the deep dive
Every other guardrail, on its own page.
- AI cost controls Autonomy you can afford.
- Human-in-the-loop Humans approve only where policy requires.
- Security Your key, your quota, your data.
- Data residency Choose what lands where.
- Claude Code & MCP Your engineers' sessions join the record.
- The deep dive All six on one page, with the roadmap and the comparison.
Put your backlog on the continuum.
From intent to PR to review — one durable, auditable continuum of work. Early access opens soon.
coming soon
Early access opens once the waitlist terms and privacy notice are final. Nothing to sign up for yet — this page collects no email.